CyyderExecutive Decision Range
Powered by the CYYDER CLARITYβ„’ Framework

CYYDER Executive Cyber Decision Range

Cyber Governance, Architecture & Technical Decision Range. Train how a CISO thinks by analyzing real business scenarios, control points, and risk trade-offs.

LAYER 1 - LAYER 7 INLINE SECURITY🟦 FOUNDATION

Lab 1 Β· Securing Data Flow Across the OSI Model

OSI 7-Layer Packet Tracer & Security Inspector

Simulate packet encapsulation top-to-bottom and evaluate inline controls including Router ACLs (L3), Stateful Firewalls (L4), and Web Application Firewalls (L7).

OSI seven layer stack with inline security controls

Business Scenario: Your organization is exposing internal web applications to external partners. Where should security controls inspect payloads without degrading network throughput?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox
SWITCH PORT SECURITY & NAC🟦 FOUNDATION

Lab 2 Β· Handling L2 MITM-Based Attacks

L2 MITM & ARP Poisoning Defense Sandbox

Analyze bidirectional ARP cache poisoning in local broadcast domains. Configure switch controls including Dynamic ARP Inspection (DAI), Sticky MAC, and 802.1X NAC isolation VLANs.

Layer 2 switch with a man-in-the-middle attacker node

Business Scenario: An unauthenticated rogue device plugs directly into an internal office switch port. How do you isolate the threat at L2 before lateral movement occurs?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox
SWG, DLP & DNS PROTECTION🟩 ENTERPRISE

Lab 3 Β· Handling Insider Threats & Content Control

Insider Threat, Web Gateway & DNS Security Sandbox

Inspect authenticated outbound user traffic. Mitigate data exfiltration to personal cloud storage via SWG/DLP, isolate risky downloads with Remote Browser Isolation (RBI), and sinkhole unauthorized DNS bypasses.

Insider threat workstation blocked by DLP and DNS controls

Business Scenario: An authenticated employee is attempting to upload sensitive customer DB files to personal cloud storage. How do you enforce DLP without blocking legitimate SaaS usage?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox
PURDUE MODEL & ICS PROTOCOL DPIπŸŸ₯ OT/SCADA

Lab 4 Β· Securing OT & SCADA Networks

OT/SCADA Industrial Cybersecurity Sandbox

Explore cyber-physical process security across Purdue Model levels. Defend OpenPLC Modbus TCP registers, enforce Industrial Deep Packet Inspection (DPI) write-blocking, and prevent process tank overfills.

Industrial SCADA tank process with PLC and DPI gateway

Business Scenario: A compromised engineering workstation sends unauthenticated commands to a water treatment PLC. How do you enforce protocol-level safety boundaries without disrupting physical operations?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox
IDENTITY ATTACK & ZERO TRUST🟩 ENTERPRISE & IDENTITY

Lab 5 Β· Identity Attack & Zero Trust

Lab 5 β€” Identity Attack & Zero Trust Decision Sandbox

Evaluate Multi-Factor Authentication (MFA), Legacy Auth blocking, Device Compliance, Geofencing, and Risk-based Adaptive Authentication to prove why Identity is the new perimeter.

Zero Trust identity controls evaluating a risky authentication attempt

Business Scenario: An employee's primary credentials (Username & Password) were leaked in a dark web dump. An external attacker attempts to log in to M365 from a high-risk IP. Can your Zero Trust Conditional Access policies block the breach?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox
EMAIL JOURNEY & PROTECTION🟩 ENTERPRISE & CONTENT SECURITY

Lab 6 Β· Email Journey & Protection

Lab 6 β€” Email Journey & Protection Decision Sandbox

Trace the full 8-stage inbound email pipeline from domain authentication (SPF/DKIM/DMARC) to SEG filtering, Attachment Sandboxing, Time-of-Click Safe Links, and EDR containment.

Eight-stage inbound email security inspection pipeline

Business Scenario: An attacker is spoofing your corporate domain (ceo@company.com) with a malicious PDF payload and a credential-harvesting link. At which stage of the inbound mail delivery pipeline will your security controls detect and block the attack?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox
SaaS SHARING, CASB & DLP🟧 CLOUD & SaaS SECURITY

Lab 7 Β· SaaS & Cloud Misconfiguration

Lab 7 β€” SaaS & Cloud Misconfiguration Decision Sandbox

Inspect external cloud sharing vulnerabilities. Test Tenant Sharing Policies, CASB Real-Time Session Controls, DLP rules, and Purview Information Protection (MIP) file-level encryption.

SaaS document sharing exposure controlled by CASB and DLP

Business Scenario: Marketing created an anonymous external share link ('Anyone with the link') on OneDrive containing sensitive customer PII. Which Cloud Control (CASB, DLP, Information Protection, or Tenant Policy) will prevent data exposure?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox
GCP SOC, THREAT HUNTING & ATT&CK CHAINS🟧 CLOUD SOC & THREAT HUNTING

Lab 8 Β· Google Cloud SOC & Threat Hunting

Lab 8 β€” Google Cloud SOC & Threat Hunting Sandbox

Explore 80 GCP detection rules, 20 threat hunting hypotheses, and 8 multi-stage attack correlation chains (IAM, GKE, BigQuery, KMS, and Cloud Audit Logs).

Google Cloud SOC dashboard with detection rules and threat hunting chains

Business Scenario: An attacker escalates IAM privileges to Organization Owner. How do you correlate Cloud Audit Logs across 4 attack stages within a 60-minute window?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox
AWS CLOUDTRAIL, GUARDDUTY & ATT&CK CHAINS🟧 CLOUD SOC & THREAT HUNTING

Lab 9 Β· AWS Cloud SOC & Incident Response

Lab 9 β€” AWS Cloud SOC & Incident Response Sandbox

Practice AWS detection engineering across 60 rules, 15 threat hunting hypotheses, and 8 correlation chains (CloudTrail, GuardDuty, IAM, S3, EC2, EKS).

AWS cloud SOC dashboard with CloudTrail, GuardDuty and attack chains

Business Scenario: An adversary assumes a cross-account role and initiates a mass S3 data download. How do you detect and automate response before exfiltration completes?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox
MAVLINK IDS, GPS SPOOFING & CTI AUTOMATIONπŸŸͺ AVIATION & CYBER-PHYSICAL

Lab 10 Β· UAV & Drone Cyber Threat Defense

Lab 10 β€” UAV & Drone Cyber Threat Defense Sandbox

Empirical cyber defense for autonomous drone ecosystems. Simulate MAVLink C2 hijacking, GPS spoofing, GCS malware, and automated STIX 2.1 feed ingestion.

UAV drone cyber defense schematic with MAVLink IDS and GPS spoofing

Business Scenario: A fleet of autonomous delivery drones experiences MAVLink command injection and GPS spoofing. How do you automate CTI feeds (STIX 2.1) to defend airborne assets?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox
LOG4SHELL, VIRTUAL PATCHING & EGRESS CONTROL🟩 ENTERPRISE SECURITY & ZERO-DAY RESPONSE

Lab 11 Β· Log4Shell Zero-Day & Compensating Controls

Lab 11 β€” Log4Shell Zero-Day & Compensating Controls Sandbox

Evaluate compensating network defenses against zero-day exploits. Test Layer 7 WAF User-Agent header inspection, Outbound Layer 4 Firewall LDAP (Port 389/1389) egress blocking, and JVM system property mitigations.

Log4Shell exploit traffic contained by WAF virtual patching and outbound LDAP egress controls

Business Scenario: A critical zero-day (Log4Shell / CVE-2021-44228) affects your unpatched production billing server. A vendor patch is 2 weeks away. Can compensating network controls (WAF Virtual Patching & Outbound L4 Egress Rules) prevent Remote Code Execution (RCE) without shutting down the application?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox
DIGITAL KYC, BIOMETRICS & AML SCREENING🟩 ENTERPRISE & IDENTITY GOVERNANCE

Lab 12 Β· Digital KYC & Biometric Identity Verification

Lab 12 β€” Digital KYC & Biometric Identity Verification Sandbox

Evaluate digital identity verification controls. Test AI ID document forensics, ISO 30107-3 dynamic liveness challenges, 3D presentation attack detection, and real-time PEP/AML sanctions screening.

Digital KYC identity document, biometric face scan, liveness detection, and AML screening pipeline

Business Scenario: Fraudsters are using deepfake videos and synthetic identities to open fraudulent accounts. At which stage of the 4-step eKYC pipeline (Data Entry, ID Capture, Biometrics, AML Watchlist) will your controls catch the attack?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox
C-SCRM, SBOM & SUPPLY CHAIN GOVERNANCE🟩 ENTERPRISE & GRC GOVERNANCE

Lab 13 Β· C-SCRM & Software Supply Chain Governance

Lab 13 β€” C-SCRM & Software Supply Chain Governance Sandbox

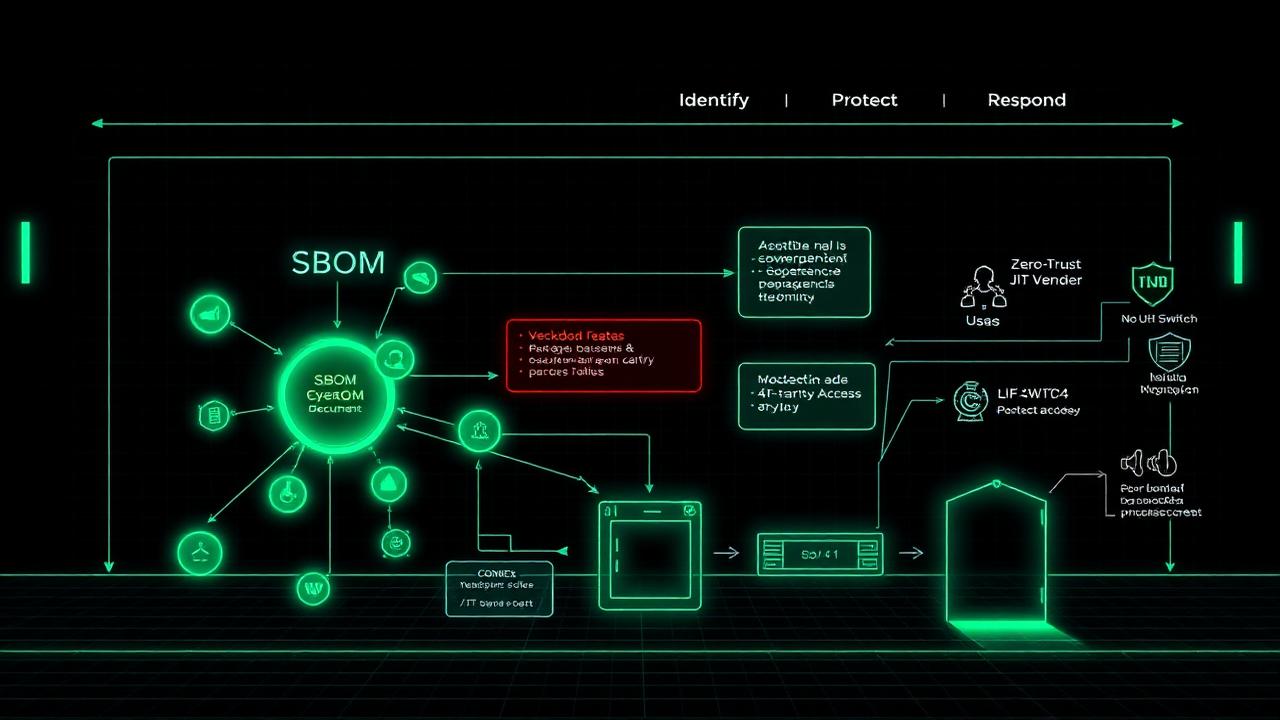
Evaluate Cyber Supply Chain Risk Management (NIST SP 800-161 / DORA). Test automated SBOM parsing (CycloneDX/SPDX), 4th-party dependency auditing, Zero-Trust JIT vendor access, and automated vendor isolation kill-switches.

C-SCRM supply chain lifecycle with SBOM parsing, dependency audit, and vendor kill-switch

Business Scenario: A key 3rd-party vendor software update embeds a backdoored 4th-party open-source dependency. At which stage of the 5-step C-SCRM lifecycle (Identify, Assess, Protect, Monitor, Respond) will your controls intercept the attack?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox
GDS, DCS & N-TH PARTY TRAVEL PIPELINEπŸŸͺ AVIATION & SUPPLY CHAIN SECURITY

Lab 14 Β· Aviation Cyber Supply Chain & GDS Integration

Lab 14 β€” Aviation Cyber Supply Chain & GDS Integration Sandbox

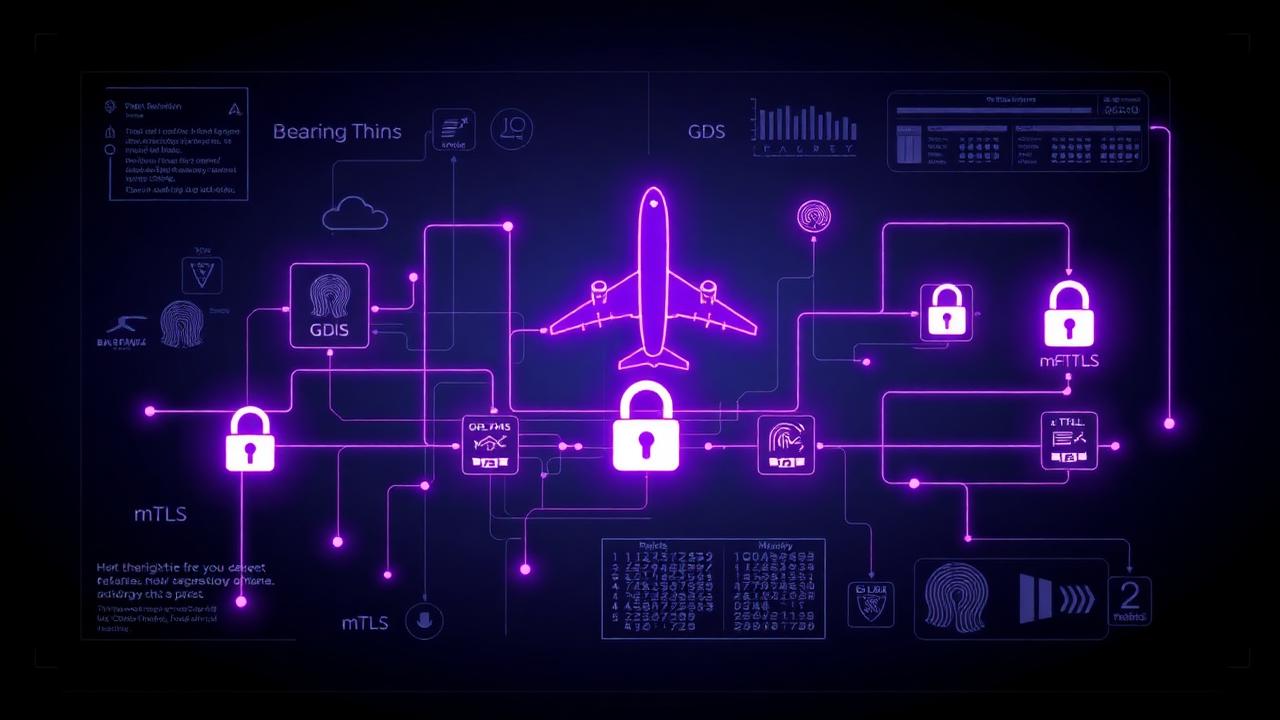
Evaluate N-th party supply chain risks in aviation and travel tech. Test Travel Agency MFA & issuance caps, Backoffice Multi-Tenant Row-Level Isolation, GDS/LDS Mutual TLS (mTLS), and Airline Departure Control System (DCS) biometric cross-matching.

Aviation travel supply chain schematic with GDS booking pipeline, mTLS locks, and biometric cross-matching

Business Scenario: A travel agency's credentials are stolen and used to execute $150K in automated issuance fraud across an aggregated B2B pipeline (Travel Booster, Amadeus/Sabre GDS, and Low-Cost Airline Direct APIs). At which tier of the 4-stage supply chain pipeline will your controls intercept the attack?

Context Landscape Alignment Risk & Control Testing
Launch Decision Sandbox